SCADA (supervisory control and data acquisition) is the system a control room uses to watch and command equipment spread over a wide area, such as a water network, a pipeline or a power grid. Controllers at each site run the equipment; SCADA collects their readings, shows them to operators, raises alarms and sends back new setpoints.
This guide explains each component and how they connect, using the definitions in NIST SP 800-82 Rev. 3, the US government’s guide to operational technology (OT) security. It also covers what most explainers skip. Which protocols SCADA actually speaks, and which have security built in. Why a SCADA scan takes seconds, not milliseconds, with the arithmetic. And the incidents that changed how these systems are protected.
What is SCADA System?
NIST describes SCADA systems as being “used to control dispersed assets for which centralized data acquisition is as important as control” (NIST SP 800-82r3, section 2.3.2). The two halves of the name are the two jobs:
- Data acquisition: collecting measurements, status and alarms from equipment at remote field sites and bringing them to one place.
- Supervisory control: sending commands and new setpoints back to those sites. NIST notes that this control “can be automatic, or it can be performed by operator commands”.
The point most explanations get wrong is who does the controlling. SCADA usually does not run the fast control loops itself. In NIST’s words, the control server stores and processes the data from the field, “while the RTU or PLC controls the local process”. SCADA supervises the controllers that do the work.
NIST lists where it is typically found: water distribution and wastewater collection, oil and natural gas pipelines, electric power transmission and distribution, and rail and other public transport. The common thread is distance: many sites, far apart, watched from one control center.
How does it work?
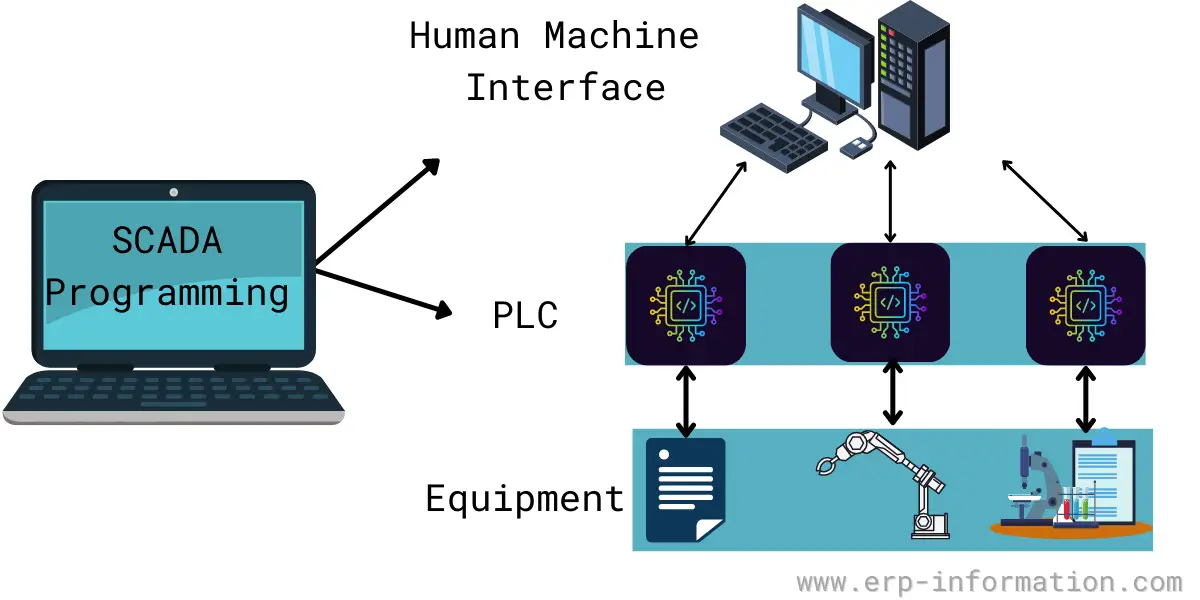
Every SCADA system runs the same loop, shown in the diagram above:
- A sensor measures a physical value. NIST’s examples are speed, temperature and flow.
- An RTU or PLC at the site reads the sensor and runs the local control logic, such as holding a value inside its limits.
- The control server collects the data. NIST describes the control center polling field devices “at defined intervals (e.g., 5 seconds, 60 seconds)” while it also watches for priority alarms from the sites.
- The HMI and the data historian display the values, store them for trends and reports, and raise an alarm when a value leaves its acceptable range.
- An operator, or a programmed rule, acts by sending a new setpoint or a command.
- The RTU or PLC carries it out by driving an actuator. NIST’s examples are control valves, breakers, switches and motors.
Polling and report by exception
Data can reach the control server in two ways. With polling, the server asks each site in turn, on a schedule. With report by exception, a site sends data on its own when something changes. DNP3, which was built for electric utilities, supports both: its primer describes an outstation that “spontaneously transmits a response without having received a specific request for the data”. Sparkplug, a specification built on MQTT for SCADA and industrial IoT, makes report by exception its normal mode and tells devices not to publish on a fixed timer.
Why a SCADA scan takes seconds: the arithmetic
Polling over a slow link is why SCADA works on a timescale of seconds. Here is our calculation for Modbus RTU, the oldest protocol in the table further down, using only figures from the Modbus Organization’s own serial line and application protocol specifications:
- Each byte travels as 11 bits: a start bit, 8 data bits, a parity bit and a stop bit. At 9,600 baud, the rate every Modbus serial device must support, one byte takes 1.146 ms.
- Frames must be separated by a silence of at least 3.5 character times.
- A request to read holding registers is 8 bytes. The reply is 5 bytes plus 2 bytes per register, and one request can ask for at most 125 registers.
| Polling 30 field devices | 9,600 baud | 19,200 baud |
|---|---|---|
| 10 registers from each | 1.4 s | 0.7 s |
| 125 registers from each | 9.3 s | 4.6 s |
One 10-register poll is 33 bytes on the wire plus two 3.5-character gaps: 40 character times, or 45.8 ms at 9,600 baud. Thirty of them take 1.4 seconds, and whatever the devices and the network add comes on top. This is why NIST’s example poll intervals are counted in seconds and large systems lean on report by exception. It is also why the fast control loops stay in the RTU or PLC at the site.
Importance of SCADA
SCADA exists because the assets it watches are too spread out to staff. Colonial Pipeline’s system, for example, runs 5,500 miles, according to its chief executive’s testimony to the US House. SCADA lets an operator “monitor or control an entire system from a central location in near real-time”, as NIST puts it, instead of sending people to each site.
The control center is also where the operation’s memory lives. NIST assigns it “centralized alarming, trend analyses, and reporting”: the alarm that reaches the night shift, the trend that shows a pump drifting, the record that answers a regulator’s question later.
And SCADA is where plant data meets the business. ISA-95 is the standard for integrating business systems with manufacturing control. ISA’s own summary of it places “manufacturing execution systems (MES) and other systems such as supervisory control and data acquisition (SCADA)” at Level 3, with enterprise resource planning (ERP) at Level 4. If you are connecting plant data to an MES or ERP system, the SCADA layer is usually where that data comes from.
SCADA system components
NIST’s glossary gives a precise meaning for each part. Here they are from the field up to the control room.
Field devices: sensors and actuators
A sensor is, in NIST’s definition, a device whose voltage or current output represents a physical property being measured, “(e.g., speed, temperature, flow)”. An actuator moves or controls a mechanism: control valves, breakers, switches and motors. Sensors are the inputs to the control system and actuators are its outputs.
Remote terminal unit (RTU)
NIST defines the RTU as “a computer with radio interfacing used in remote situations where communications via wire is unavailable”, used to talk to remote field equipment. It adds that “PLCs with radio communication capabilities are also used in place of RTUs”, which is why the two names are often used loosely.
Programmable logic controller (PLC)
A PLC is a solid-state controller with user-programmable memory for logic, timing, counting, PID control and communications. According to NIST, “PLCs are used in both SCADA and DCS systems as the control components of an overall” hierarchical system. In SCADA they can do the job of an RTU.
Intelligent electronic device (IED)
An IED, such as a protective relay, contains its own processor. It can report straight to the control server or be polled by a local RTU. In most cases it also has local programming that lets it act without instructions from the control center.
Communication network
Links between the control center and the field use telemetry over telephone line, cable, fiber and radio (broadcast, microwave, satellite), according to NIST; its general SCADA layout also shows cellular. Communications routers connect the control center’s local network to the wide area network and to the field sites.
Control server (MTU)
The central computer that polls the field, stores and processes the data and issues commands. In a SCADA system it is “often called a SCADA server, MTU, or supervisory controller”, per NIST. MTU stands for master terminal unit.
Human-machine interface (HMI)
The screens operators use. NIST defines the HMI as “the hardware or software through which an operator interacts with a controller”. ISA-101.01-2015 is the standard for designing process HMIs, covering screen navigation, graphics and color conventions.
Data historian
“A centralized database that supports data analysis using statistical process control techniques”, in NIST’s words. It is the record that trends, reports and investigations draw on.
Engineering workstation
The computer engineers use to configure the system and program the controllers. In NIST’s PLC example, “the PLC is accessible via a programming interface located on an engineering” workstation. This is a separate tool from the HMI: operators run the process from the HMI; engineers change the logic from the workstation.
SCADA system architecture
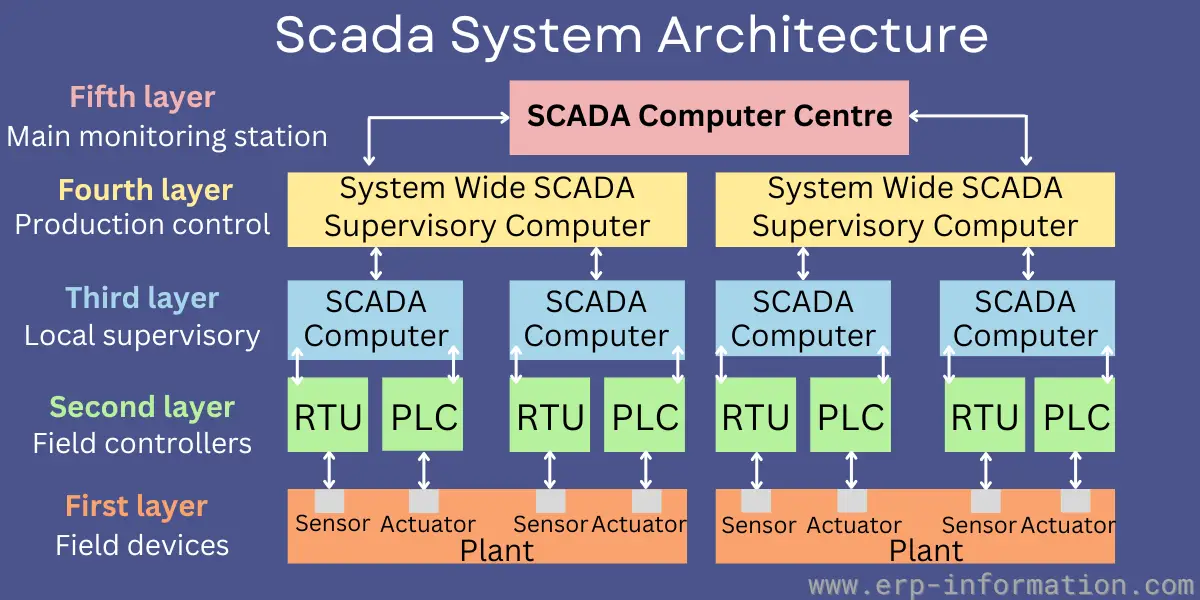
The diagram above follows NIST’s general SCADA layout. Read it from the bottom. Sensors and actuators connect to controllers at each field site. The controllers reach the control center over a communications network. Inside the control center, the control server, HMI, data historian and engineering workstation share a local network. Readings, status and alarms travel up. Commands and setpoints travel down.
Large systems add a middle tier
“Large SCADA systems that contain hundreds of RTUs often employ a sub-control server” to take load off the primary server, according to NIST. In NIST’s example, each sub-SCADA server handles its own group of field sites and connects to the main SCADA server.
Communication topologies
NIST, citing the American Gas Association’s Report No. 12, names four basic ways to wire the field sites to the center:
- Point-to-point: one channel per site. The simplest, but it can be expensive because every connection needs its own channel.
- Series: sites share one channel in a chain. Fewer channels, but sharing affects efficiency and complexity.
- Series-star and multi-drop: NIST notes these also cost efficiency and add complexity.
Where SCADA sits in the Purdue model and ISA-95
Ask two sources which level SCADA belongs to and you can get two answers. NIST’s Purdue model figure puts the operator HMI at Level 2, area control. ISA’s summary of ISA-95 puts SCADA with MES at Level 3, and puts PLCs and DCSs at Level 2. Both models stack the same things in the same order; they slice them differently. When a vendor, auditor or network designer asks which level, ask which model they mean.
| Level | NIST Purdue model (Fig. 16) | ISA-95 (ISA summary) |
|---|---|---|
| 4 | Business planning and logistics | Business planning and logistics, including ERP |
| 3 | Operations and control | Manufacturing operations: MES and SCADA |
| 2 | Area control (HMI) | Monitoring and supervising: PLCs, DCSs |
| 1 | Controller network | Sensing and manipulating: sensors, valves |
| 0 | Field I/O devices | Physical production processes |
For security the model is used to separate traffic. NIST recommends firewall rules that stop Level 4 business devices from talking directly to Levels 2, 1 and 0, with a DMZ between the business network and the control network.
SCADA communication protocols
SCADA is held together by its protocols, and most of them were designed before anyone expected an attacker on the network. NIST puts it bluntly: “OT protocols often have few or no security capabilities”. The table shows the main ones and where security comes from for each, checked against each standard’s owner on 14 October 2026.
| Protocol | Where it is used | Security |
|---|---|---|
| Modbus (Modicon, 1979; TCP port 502) | Industry-wide; RTUs over radio, oil and gas, substations | None in the base protocol. Modbus/TCP Security wraps it in TLS on port 802 |
| DNP3 (IEEE 1815) | Electric and water utilities; also transport, oil and gas | Secure Authentication (SAv5); the newer DNP3-SL adds encryption |
| IEC 60870-5-101 / -104 | Telecontrol of widespread processes, mainly power | Out of scope of -104 itself; added by IEC 62351-5:2023 and IEC TS 60870-5-7:2025 |
| IEC 61850 | Communication between IEDs in power utility automation | IEC 62351 series |
| OPC UA (IEC 62541) | Machine-to-machine and machine-to-enterprise data exchange | Built in: authentication, signing, encryption |
| MQTT with Sparkplug 3.0 | SCADA and IIoT, report by exception | TLS (port 8883) |
What changed recently
- Modbus: the Modbus Organization’s secure variant, Modbus/TCP Security, wraps Modbus in TLS and uses X.509v3 certificates to authenticate both ends.
- DNP3: IEEE 1815-2012 has been listed as Inactive-Reserved since 30 March 2023, because it was not revised within ten years; a revision project (P1815) has been open since 2015. The DNP Users Group’s newer DNP3 Security Layer (DNP3-SL, formerly SAv6) implements IEC 62351-5 and adds message encryption.
- IEC 60870-5-104: the standard says outright that “security mechanisms are outside the scope of this standard”. IEC TS 60870-5-7:2025 now specifies how to add IEC 62351-5 security to -101 and -104.
- OPC UA: the IEC published IEC 62541-1:2025 in December 2025. OPC UA’s security modes are None, Sign and SignAndEncrypt, and the OPC Foundation’s specification requires the None profile to be disabled by default.
- Sparkplug: the Eclipse Foundation announced in November 2023 that Sparkplug 3.0 had been published as international standard ISO/IEC 20237.
SCADA vs PLC vs DCS
All three appear in most large plants, and the confusion comes from the PLC being inside the other two. NIST separates them by scope. A PLC is a controller. A DCS controls production “within the same geographic location”, such as a refinery, a power station or a chemical plant. SCADA supervises assets spread across a wide area.
| PLC | DCS | SCADA | |
|---|---|---|---|
| What it is | A programmable controller | A plant-wide control system | A supervisory system over many sites |
| Scope | Local: a machine or process | One plant or location | Dispersed sites, often far apart |
| Closes the control loop? | Yes, locally | Yes, with a supervisory loop over local controllers | Usually no: the RTU or PLC does |
| Data to the operator | Often no central HMI | Supervisory level within the plant | Polled at intervals or by exception |
| Typical users | Assembly lines, machines | Refineries, power plants, chemicals, pharma | Water networks, pipelines, power grids, rail |
Two things blur the lines in practice. SCADA and DCS are often networked together, NIST says: a power company may run its generation plants on a DCS and its transmission and distribution grid on SCADA. And a PLC can work as a SCADA field controller, a DCS local controller, or on its own running an assembly line.
One correction to a common claim, including an earlier version of this page: a DCS is not what keeps a hazardous plant safe. That job belongs to a separate safety instrumented system (SIS), designed to IEC 61511. NIST notes that an SIS is often kept independent of the basic process control system, so that a failure of the control system does not stop the safety function.
Examples of SCADA system
The sectors below are the ones NIST names for SCADA. Each example is a documented system or event, not a hypothetical.
1. Electric power transmission and distribution
Grid operators use SCADA to watch substations and operate breakers remotely. The 2015 attack on three Ukrainian distribution companies, analysed by CISA and the E-ISAC with SANS, shows how much that control matters. Attackers used remote access to the utilities’ control software to open breakers, cutting power to about 225,000 customers. Common substation protocols include DNP3, IEC 60870-5-104 and IEC 61850.
2. Water distribution and wastewater
Water utilities use SCADA to run pumps, valves and treatment across their networks. CISA’s 2023 advisory on attacks against water facilities describes US water and wastewater systems that “operate HMI-capable Unitronics Vision Series PLCs”, controllers with their own built-in operator screen.
3. Oil and gas pipelines
In May 2021, ransomware hit Colonial Pipeline’s IT network. The company shut down all 5,500 miles of pipeline as a precaution, so the malware could not spread to the operational technology network that runs it.
4. Rail and public transport
NIST includes a rail monitoring and control SCADA example in SP 800-82r3, and lists rail and other public transport among SCADA’s typical uses.
5. Manufacturing
In factories, PLCs run machines and lines while SCADA or an MES supervises them at ISA-95 Level 3, between the plant floor and ERP. NIST’s own example of a PLC-only system is an automobile assembly line. That shows where the boundary sits: one site needing fast closed-loop control is PLC territory, while many sites needing central supervision is SCADA territory.
SCADA Implementation Steps
A SCADA project is mostly decisions made before any software is installed. This order follows the standards each step depends on.
- List what you must see and control, at which sites, and how fresh the data must be. The poll-time arithmetic above decides whether polling is fast enough or you need report by exception.
- Choose protocols with a secure option that your field devices support: Modbus/TCP Security, DNP3 Secure Authentication or DNP3-SL, IEC 62351 for IEC protocols, or OPC UA with signing and encryption.
- Design the network in zones. Separate the control network from the business network with a DMZ, and block direct paths from business systems to the controllers, as NIST and CISA both recommend.
- Write an alarm philosophy before configuring alarms. ANSI/ISA-18.2-2016 (IEC 62682:2022 internationally) covers the whole alarm lifecycle, from identification and rationalization to maintenance.
- Design the HMI to ISA-101.01-2015, which covers menu hierarchies, navigation, graphics and color conventions.
- Build the security program to ISA/IEC 62443. ISA lists ANSI/ISA-62443-2-1-2024 for the asset owner’s security program and ISA-62443-3-3-2013 for system security requirements.
- Keep safety separate. Where a process can hurt people, its safety functions belong in a safety instrumented system designed to IEC 61511, not in SCADA.
- Never put a controller or HMI on the public internet, and change every default password. Both are the first items in CISA’s 2025 guidance (see the security section).
- Practise running without it. CISA’s advice is to “practice and maintain the ability to operate OT systems manually”.
History of SCADA
A 2004 US government technical bulletin, from the National Communications System (NCS TIB 04-1), states that SCADA has been used by US utilities since the 1960s, with origins in early telemetry. The same bulletin, drawing on a 2002 IEEE conference paper, describes three generations:
- Monolithic: mainframe-era systems that stood alone; networks were generally non-existent.
- Distributed: local area networks and smaller computers spread the processing across several machines.
- Networked: open architecture replaced vendor-controlled, proprietary environments.
Later academic reviews add a fourth, Internet of Things or cloud-based, generation. That label is useful but informal: we found no standards body or government source that defines it. No primary source we found gives firm dates for each generation either, so treat decade-by-decade timelines you see elsewhere as approximate.
| Year | Milestone |
|---|---|
| 1960s | SCADA in use at US utilities (NCS, 2004) |
| 1979 | Modicon introduces Modbus |
| 1993 | DNP3 passed from Harris to the DNP Users Group |
| 2008 | OPC UA released |
| 2010 | First ICS-CERT advisories on Stuxnet; DNP3 first adopted as IEEE 1815 |
| 2015 | Ukraine grid attack via SCADA |
| 2023 | NIST SP 800-82 Rev. 3; Sparkplug 3.0 becomes ISO/IEC 20237 |
| 2026 | NIST SP 800-82 Rev. 4 draft (21 September) |
SCADA security: the risk of connecting OT to IT
SCADA was built for availability and reliability, not for a hostile network. The US Department of Energy’s 21 Steps to Improve Cyber Security of SCADA Networks said so in 2002: these networks were “designed to maximize functionality, with little attention paid to security”. As they connected to business networks and remote access, that gap became the main risk.
Five incidents and what each one taught
| Year | What happened | The lesson |
|---|---|---|
| 2010 | Stuxnet changed code on Siemens PLCs and replayed recorded normal values to the operator screens (Symantec, Langner) | The HMI can show normal while the process is not |
| 2015 | Attackers used remote access to the control software of three Ukrainian utilities to open breakers; about 225,000 customers lost power (CISA) | Remote access is the door |
| 2021 | Ransomware hit Colonial Pipeline’s IT network; the pipeline was shut down as a precaution (CEO testimony; CISA) | OT can stop even when only IT is hit |
| 2023 | Internet-exposed Unitronics PLCs with default passwords were defaced: at least 75 devices, at least 34 of them in US water systems (CISA, Treasury) | Exposure plus default passwords is enough |
| 2025 | Pro-Russia hacktivists used internet-facing VNC to reach OT control devices (CISA AA25-343A) | Remote screen-sharing is remote control |
Two details matter more than the headlines. In Stuxnet, Ralph Langner’s analysis notes that the process manipulations occurred on “controllers, not on SCADA systems”, while recorded values were played back to the operator screens. And in the 2023 water attacks, the US Treasury said “this particular operation did not disrupt any critical services”; the affected water authority took the system offline and switched to manual operation.
One widely repeated story needs a correction. The 2021 Oldsmar, Florida water treatment case was reported as a remote hack of a SCADA system. CISA’s own advisory now adds that “the FBI was not able to confirm that this incident was initiated by a targeted cyber intrusion” (AA21-042A). It should not be cited as a confirmed attack.
SCADA and PLC products on CISA’s exploited-vulnerabilities list
CISA’s Known Exploited Vulnerabilities catalog lists flaws with evidence of real-world exploitation. We downloaded catalog version 2026.10.13 (1,741 entries) and read every vendor name. Nine entries are industrial or building control products: SCADA software, HMIs, PLCs or their modules.
| Product | Flaw | Added |
|---|---|---|
| Rockwell, multiple Logix products | Insufficiently protected credentials | Mar 2026 |
| OpenPLC ScadaBR | Unrestricted file upload | Dec 2025 |
| OpenPLC ScadaBR | Cross-site scripting | Nov 2025 |
| Unitronics Vision PLC and HMI | Insecure default password | Dec 2023 |
| Delta Electronics DOPSoft 2 (HMI) | Improper input validation | Aug 2022 |
| Schneider Electric U.motion Builder | SQL injection | Apr 2022 |
| Trihedral VTScada | Denial of service | Apr 2022 |
| InduSoft Web Studio | Directory traversal | Apr 2022 |
| Siemens SIMATIC CP 1543-1 | Improper privilege management | Mar 2022 |
Two readings of that table. First, none of the nine is flagged for known ransomware use, against 361 of the catalog’s 1,741 entries. Second, the list is far from complete for this sector: CISA’s August 2026 advisory AA26-231A describes attackers targeting Siemens S7 PLCs, yet the catalog holds only one Siemens entry. Treat KEV as a floor, not a full count.
What current guidance says
- In May 2025, CISA, FBI, EPA and DOE published Primary Mitigations to Reduce Cyber Threats to Operational Technology. It lists five steps in this order: “remove OT connections to the public internet”, change default passwords, secure remote access, segment IT and OT networks with a DMZ, and practise operating manually.
- The August 2026 advisory on Siemens S7 PLCs reports attackers using AI-generated exploit scripts disguised as monitoring tools, and tells owners to block TCP port 102 at perimeter firewalls.
- In September 2026 the FBI and CISA published a fact sheet on working with third-party ICS integrators. It describes a 2025 breach at an integrator in which attackers packaged customer SCADA information for presumed theft.
- NIST SP 800-82 Rev. 3 (September 2023) is the current final guide. A Rev. 4 draft was published on 21 September 2026, with comments due by 30 November 2026.
Benefits and limitations of SCADA
Benefits
- One view of dispersed assets: operators monitor and control a whole network from a central location, in near real time.
- Automatic or operator control: depending on the setup, each control action can run automatically or wait for an operator’s command.
- Alarms, trends and records in one place: centralized alarming, trend analysis and reporting are core control center functions.
- Built for uptime: NIST notes SCADA systems are usually designed to be fault-tolerant, with significant redundancy.
- A data source for the business: the same data feeds MES and ERP at ISA-95 Levels 3 and 4, and IIoT platforms through specifications such as Sparkplug.
Limitations
- Seconds, not milliseconds: polled data can be seconds old (see the arithmetic above), so fast control must stay local.
- Legacy protocols: many field protocols have no authentication or encryption unless a secure variant is deployed.
- A larger attack surface once connected: remote access, internet exposure and default passwords were the entry points in the incidents above.
- Redundancy is not security: NIST warns that redundancy may not be a sufficient countermeasure against a malicious attack.
FAQs
What is the full form of SCADA?
SCADA stands for supervisory control and data acquisition. Data acquisition is collecting readings and alarms from remote field sites; supervisory control is sending commands and setpoints back to the controllers at those sites.
Is SCADA hardware or software?
Both. The control server, HMI and data historian are software running on computers in a control center, and they depend on hardware in the field: RTUs, PLCs and IEDs, plus the communication network that links them. NIST describes SCADA as integrating data acquisition systems with data transmission systems and HMI software.
What is the difference between SCADA and PLC?
A PLC is a controller that runs a machine or process locally. SCADA is the supervisory layer above many controllers: it collects their data, shows it to operators and sends them new setpoints. In a SCADA system, the RTU or PLC controls the local process and SCADA supervises it.
What is the difference between SCADA and DCS?
NIST separates them by geography. A DCS controls production within the same geographic location, such as a refinery or power station. SCADA supervises dispersed assets such as pipelines, water networks and power grids. The two are often networked together, for example a DCS in a power plant and SCADA on the grid it feeds.
Where does SCADA sit in the Purdue model?
It depends on the model. NIST’s Purdue figure places the operator HMI at Level 2, area control, while ISA’s summary of ISA-95 places SCADA with MES at Level 3, above PLCs and DCSs at Level 2. Ask which model a vendor or auditor is using.
Is SCADA a cybersecurity risk?
It can be. Many SCADA protocols were designed without authentication or encryption, and connecting SCADA to business networks and the internet removed the isolation it once relied on. CISA’s 2025 guidance starts with removing OT connections to the public internet and changing default passwords.
Before you choose or design a SCADA system
Five questions settle most SCADA designs, and they are worth answering before you compare products:
- How many sites, how far apart, and what links can reach them (fiber, radio, cellular, satellite)?
- How fresh must the data be? Run the poll-time arithmetic; if polling is too slow, require report by exception.
- Which protocols do your field devices speak, and does each one have a secure variant you can turn on?
- Where will SCADA sit in your network zones, and what stands between it and the business network?
- If SCADA goes down tomorrow, can your staff run the process by hand?
How we researched this page (checked 14 October 2026). Definitions and the architecture come from NIST SP 800-82 Rev. 3 and ISA’s standards pages. Protocol facts come from each protocol’s owner: the Modbus Organization, the DNP Users Group, IEEE, the IEC webstore, the OPC Foundation, OASIS and the Eclipse Foundation. Incidents come from CISA and FBI advisories, Symantec’s and Langner’s technical analyses and sworn testimony, and were re-checked against later corrections. The poll-time table is our calculation from the Modbus specifications. The KEV table is our selection from CISA’s catalog. We kept entries whose vendor, product or description names SCADA, HMI or PLC products or an industrial control vendor. We removed false matches, such as Ivanti Connect Secure (abbreviated ICS), and read every vendor name for misses. The diagrams on this page are our own, drawn from the NIST text. An earlier version of this page had four errors, now corrected: it called valves and actuators input devices, described the HMI under field controllers, showed an invented fifth architecture layer, and said a DCS is what keeps hazardous plants safe.
References
- NIST SP 800-82 Rev. 3, Guide to Operational Technology (OT) Security (September 2023)
- NIST SP 800-82 Rev. 4, initial public draft (21 September 2026)
- ISA: ISA-95 series of standards, Enterprise-Control System Integration
- ISA: ISA-18 series, ANSI/ISA-18.2-2016 Management of Alarm Systems for the Process Industries
- ISA: ISA-101 series, ISA-101.01-2015 Human Machine Interfaces for Process Automation Systems
- ISA: ISA/IEC 62443 series of standards
- IEC 61511-1:2016+AMD1:2017, Functional safety: Safety instrumented systems for the process industry sector
- Modbus Organization: Modbus specifications (application protocol V1.1b3, serial line V1.02, Modbus/TCP Security)
- Modbus Organization: MODBUS over Serial Line, Specification and Implementation Guide V1.02 (2006)
- Modbus Organization: MODBUS Application Protocol Specification V1.1b3 (2012)
- DNP Users Group: Overview of the DNP3 protocol
- DNP Users Group: A DNP3 Protocol Primer, Rev A (2005)
- IEEE 1815-2012, Standard for Electric Power Systems Communications: DNP3 (Inactive-Reserved since 2023-03-30)
- IEC 60870-5-104:2006+AMD1:2016, Network access for IEC 60870-5-101 using standard transport profiles
- IEC TS 60870-5-7:2025, Security extensions to IEC 60870-5-101 and IEC 60870-5-104 protocols
- IEC 62351-5:2023, Security for IEC 60870-5 and derivatives
- IEC 61850 series, Communication networks and systems for power utility automation
- OPC Foundation: Unified Architecture (OPC UA)
- IEC 62541-1:2025, OPC Unified Architecture, Part 1: Overview and concepts
- OASIS: MQTT Version 5.0 (OASIS Standard, 7 March 2019)
- Eclipse Foundation: Sparkplug Specification 3.0.0
- National Communications System, Technical Information Bulletin 04-1: Supervisory Control and Data Acquisition (SCADA) Systems (October 2004)
- US Department of Energy: 21 Steps to Improve Cyber Security of SCADA Networks (2002)
- Falliere N, Murchu LO, Chien E. W32.Stuxnet Dossier, version 1.4 (Symantec, February 2011)
- Langner R. To Kill a Centrifuge (2013, archived copy)
- CISA (ICS-CERT) IR-ALERT-H-16-056-01: Cyber-Attack Against Ukrainian Critical Infrastructure
- E-ISAC and SANS ICS: Analysis of the Cyber Attack on the Ukrainian Power Grid (March 2016, archived copy)
- Blount J. Testimony to the US House Committee on Homeland Security (9 June 2021)
- CISA and FBI AA21-131A: DarkSide Ransomware
- CISA AA21-042A: Compromise of U.S. Water Treatment Facility
- CISA alert: Exploitation of Unitronics PLCs used in Water and Wastewater Systems (28 November 2023)
- CISA and partners AA23-335A: IRGC-Affiliated Cyber Actors Exploit PLCs in Multiple Sectors
- US Treasury press release JY2072 (February 2024)
- CISA and partners AA25-343A: Pro-Russia hacktivists conduct opportunistic attacks against critical infrastructure (December 2025)
- NSA, CISA, FBI, DOE and EPA AA26-231A: Siemens S7 PLCs (August 2026)
- CISA, FBI, EPA and DOE: Primary Mitigations to Reduce Cyber Threats to Operational Technology (May 2025)
- FBI and CISA: Considerations for critical infrastructure operators working with third-party ICS integrators (September 2026)
- CISA Known Exploited Vulnerabilities catalog, version 2026.10.13
Using Google Search? Add erp-information.com as a preferred source.